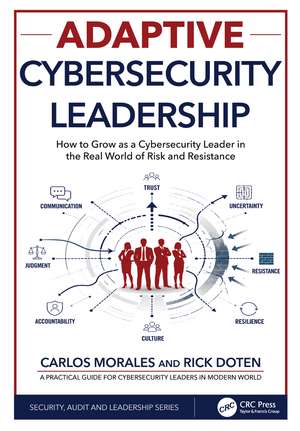
Adaptive Cybersecurity Leadership: How to Grow as a Cybersecurity Leader in the Real World of Risk and Resistance: Security, Audit and Leadership Series
Autor Carlos Morales, Rick Dotenen Limba Engleză Paperback – 4 feb 2027
For years, cybersecurity professionals have been taught how to earn a seat at the executive table, communicate with boards, and speak the language of business. Far less attention has been given to what happens after you become responsible for a team, a program, or an entire cybersecurity function.
How do you lead people under pressure without becoming the bottleneck? How do you create psychological safety while preserving accountability? How do you recognize burnout, communicate risk through resistance, develop judgment in others, and build a program that does not depend on one person repeatedly saving the day?
Adaptive Cybersecurity Leadership addresses the human and organizational side of cybersecurity leadership that most technical training leaves untouched. Drawing on years of leading and advising cybersecurity teams and programs, Carlos Morales and Rick Doten share real-world stories, practical guidance, and lessons learned from both success and failure.
The book explores how to build trust, lead through ambiguity, manage your own reactions, work with people who think differently, navigate decisions without clean answers, and adapt as AI changes the nature of work, expertise, accountability, and leadership itself.
Whether you are preparing for your first management role or already carrying responsibility for a cybersecurity function, this book will help you understand what the moment requires, adapt your approach, and build teams capable of thinking, deciding, and growing without waiting for you.
Inside, you will learn how to:
· Move from technical expert to cybersecurity leader without losing your credibility
· Communicate risk in ways that help people decide, not just understand
· Build trust, accountability, and psychological safety in your teams
· Recognize resistance, burnout, and emotional pressure before they damage performance
· Develop judgment in others instead of taking the work back yourself
· Adapt leadership practices as AI changes work, expertise, and accountability
You learned how to protect systems. Now learn how to lead the people and decisions that protect your organization.
Din seria Security, Audit and Leadership Series
-
 Preț: 418.53 lei
- 8%
 Preț: 445.18 lei
- 11%
 Preț: 635.66 lei
-
 Preț: 414.87 lei
-
 Preț: 430.76 lei
- 8%
 Preț: 438.04 lei
- 20%
 Preț: 405.06 lei
- 20%
 Preț: 1197.18 lei
-
 Preț: 322.00 lei
-
 Preț: 415.48 lei
- 20%
 Preț: 358.81 lei
- 20%
 Preț: 685.25 lei
- 20%
 Preț: 418.05 lei
- 15%
 Preț: 447.64 lei
- 20%
 Preț: 506.49 lei
- 20%
 Preț: 535.60 lei
- 20%
 Preț: 299.76 lei
- 20%
 Preț: 1629.80 lei
-
 Preț: 345.94 lei
- 20%
 Preț: 526.36 lei
-
 Preț: 384.37 lei
-
 Preț: 219.16 lei
- 20%
 Preț: 492.86 lei
- 20%
 Preț: 527.83 lei
- 20%
 Preț: 1308.63 lei
- 20%
 Preț: 354.29 lei
- 20%
 Preț: 374.75 lei
- 20%
 Preț: 1030.95 lei
- 20%
 Preț: 530.01 lei
- 20%
 Preț: 554.82 lei
- 20%
 Preț: 349.28 lei
-
 Preț: 350.55 lei
- 20%
 Preț: 311.00 lei
- 20%
 Preț: 715.46 lei
- 20%
 Preț: 488.00 lei
-
 Preț: 297.38 lei
-
 Preț: 391.02 lei
- 20%
 Preț: 316.61 lei
-
 Preț: 424.04 lei
-
 Preț: 346.21 lei
- 20%
 Preț: 327.92 lei
- 20%
 Preț: 1112.87 lei
- 20%
 Preț: 511.34 lei
Preț: 348.05 lei
Preț vechi: 392.07 lei
-11% Precomandă
Puncte Express: 522
Carte nepublicată încă
Livrare prin curier în România Precomanda se expediază când titlul devine disponibil.
Transport gratuit de la 400.00 lei Plată online sau ramburs, în funcție de opțiunile comenzii.
Retur gratuit în 14 zile Comandă securizată și suport în română.
Doresc să fiu notificat când acest titlu va fi disponibil:
Se trimite...
Specificații
ISBN-13: 9781041155232
ISBN-10: 1041155239
Pagini: 304
Ilustrații: 96
Dimensiuni: 178 x 254 mm
Ediția:1
Editura: CRC Press
Colecția CRC Press
Seria Security, Audit and Leadership Series
ISBN-10: 1041155239
Pagini: 304
Ilustrații: 96
Dimensiuni: 178 x 254 mm
Ediția:1
Editura: CRC Press
Colecția CRC Press
Seria Security, Audit and Leadership Series
Public țintă
Professional Practice & Development, Professional Reference, and Professional TrainingCuprins
Section I: Leadership Challenge: Matching Style to Context. Chapter 1: What It Really Takes to Lead Cybersecurity. Chapter 2: Leadership Modes: Building, Maintaining, Transforming, Crisis Management. Chapter 3: Matching Leadership Approach to Program and Organizational Maturity. Chapter 4: The Shift from Expert to Enabler. Section II: Building the Skills That Make Leadership Work in Cybersecurity. Chapter 5: Core Skills for Effective Cybersecurity Leadership. Chapter 6: The Behaviors That Make Leadership Work. Chapter 7: Strategic Thinking, Framing, and Influence. Chapter 8: Emotional Intelligence, Self-Regulation, and Decision Making Under Pressure. Chapter 9: Coaching, Growing, and Managing Cybersecurity Teams. Chapter 10: Leading with Awareness: Unleashing Neurodiversity and Cognitive Differences Potential. Section III: Facing the Friction: Resistance, Complexity, and the Weight of Leadership. Chapter 11: Understanding Resistance and Navigating Organization Dynamics. Chapter 12: Driving Change with Purpose: The Curve of Change. Chapter 13: Dealing with Uncertainty, Failure, and Conflict. Chapter 14: The Weight of Responsibility: Over-Confidence, Self-Doubt, Ego Traps, Bias, and Burnout. Section IV: Making It Count: Leadership at the Point of Decision. Chapter 15: Making Hard Calls: Trade-Offs, Priorities, and Integrity. Chapter 16: Using Metrics to Support the Story and Drive Alignment. Chapter 17: Communicating Risk with Clarity: Talking to Executives and the Board. Section V: Leading for the Long Haul. Chapter 18: Building Credibility, Trust, and Strong Relationships. Chapter 19: Developing Teams and Scaling Leadership Through Champions. Chapter 20: Community Outreach: How to Engage in Cybersecurity Community Locally and Industry Wide. Chapter 21: Feedback Loops, Learning Cycles and Program Sustainability. Chapter 22: Succession, Legacy and Leaving Things Better Than You Found Them. Epilogue Chapter 23: Closing Reflection.
Notă biografică
Carlos Morales, MBA, C|CISO, CISM, CRISC, and CDPSE, is a cybersecurity executive, author, and educator with more than 20 years of experience across information security, technology risk, privacy, compliance, and operational resilience. He has led cybersecurity and risk functions in multinational, highly regulated, and operationally complex environments, with responsibilities spanning enterprise technology and operational technology.
Throughout his career, Carlos has built and transformed cybersecurity teams, governance structures, risk management programs, and capabilities that connect security with business priorities. His experience includes working with organizations ranging from startups to large global enterprises across different industries and countries. This broad perspective has shaped his pragmatic approach to leadership and his belief that lasting cybersecurity results depend on sound judgment, trusted relationships, clear ownership, and the ability to help others make better decisions.
Carlos contributed from the private sector to the development of Mexico’s National Cybersecurity Plan, an initiative led by the Executive Office of the President of Mexico. He was also a member of the first Cybersecurity Innovation Council organized by the Organization of American States, where he contributed to dialogue and collaboration among cybersecurity leaders from across the Americas.
At Tecnológico de Monterrey, Carlos contributed to the development of the Cybersecurity HUB and the master’s degree in cybersecurity. He continues to teach and mentor cybersecurity professionals as a Professor of Practice, helping practitioners connect technical knowledge with business judgment, leadership, and real-world decision-making.
Carlos is the author of Cyber Risk Management in Practice: A Guide to Real-World Solutions. His work reflects a consistent philosophy: remain curious, treat people with respect, communicate risk in ways others can use, and develop teams and organizations that do not depend on individual heroics to succeed.
Rick Doten, CISSP, CISM, CCSK, is a retired award-winning CISO who now advises Boards of Directors, and organizations around the world how to mature their AI and cybersecurity programs. He is based in Charlotte, NC and known as “cruise director” for local CISO community; as he manages the calendar of events for his peers.
Rick is a frequent speaker at cybersecurity conferences such as RSA, Secureworld, Bsides, and FutureCon, and guest on numerous cybersecurity podcasts, including The CyberWire Hashtable, CISO Series, Google Cloud, Elevate Your Career, and The Rsnake Show. Rick talks about topics ranging from cybersecurity and risk, AI Governance, neurodiversity, leadership, and staffing.
In his prior role, Rick worked as Virtual CISO supporting international companies. During that time Rick educated corporate boards, developed and matured security programs, and created the curriculum for a Cybersecurity Master’s degree program for an International University.
He on the Cloud Security Alliance (CSA) CXO Trust Advisory Council, and the Boards of his local Charlotte ISC2, Bsides, and CSA Chapters. He works with several Venture Capital and go-to-market firms reviewing security technology, as well as on the Board of Advisors for several startups.
Rick is on the CIS Critical Security Controls editorial panel and was a lead author on Version 8 of the Controls. He was also on the committee to update Cloud Security Alliance CCSK v5 study guide, and create the new CSA AI certification CAISK. Rick has a Cybersecurity YouTube channel where he has videos on the 18 CIS CSC v8 Controls, and other videos on cybersecurity topics.
Rick has alternated between being a cybersecurity management consultant and CISO throughout his 27+ year cybersecurity career, and has led several ethical hacking, incident response and forensics, and risk management teams.
Descriere
Cybersecurity professionals build their careers by finding answers, solving problems, and becoming the person others call when something goes wrong. Then the role changes. Your value begins less on being the expert with the answer and more on helping others understand risk, make decisions, accept responsibility.